KD-PQ-CY-013
Cyber Security Policy
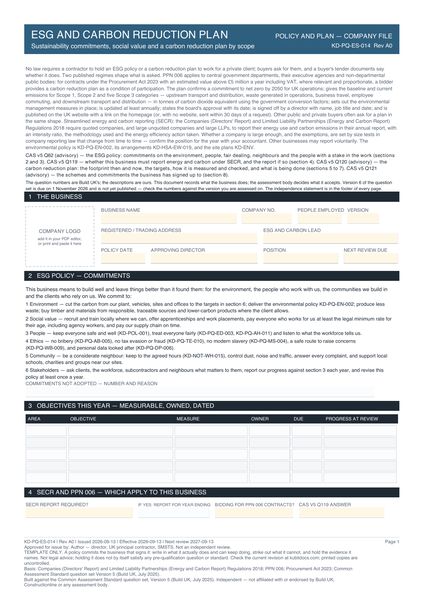
The cyber security policy for a contractor: the systems and data that matter, the rules for accounts and multi-factor authentication, devices and updates, backups of critical systems with restore tests, access control, logging and monitoring, phishing and payment fraud, home and site working, supplier access, and an incident response plan with a log — organised around the NCSC 10 Steps and the Cyber Essentials controls in our own words. Built against CAS v5 Q163.
3 pages · 127 fillable fields · works in Adobe Reader, Preview, Chrome, or on a phone — or complete it online in your browser and download the finished document.
Page 1 of 3 — click to enlarge
Read all 3 pages first — watermarked sample, no email Before you submit: the checklist
Statutory basis, cited on the form
- UK GDPR Article 32
- 10 Steps to Cyber Security (NCSC)
- Cyber Essentials (NCSC)
- Common Assessment Standard question set Version 5 (Build UK, July 2025)
What it is not
It is not a completed document and it is not health and safety advice. You must adapt it to your site and have a competent person complete and sign it off. See why we don't say "compliant".
Format
AcroForm fillable PDF. Every field has a tooltip. Tab order follows the reading order. Works on desktop and mobile, in Adobe and non-Adobe readers.
This revision was prepared against legislation current at 10 August 2026. Revision A0. Check kubitdocs.com/revisions for the current revision before use.
More in Company policies
18 documents